WEBSITES / APPS / DATA-DRIVEN BUSINESSES
Clarity about your data.
Confidence in your disclosures.
Your privacy policy should explain what your business actually does with personal information.
RICHT drafts and reviews privacy policies for websites and apps, connecting legal requirements with your products, technology, and operations. We help you identify the disclosures you need, avoid promises you cannot support, and coordinate the policy with your cookies, consent tools, and related agreements.
New policies. Existing notices. Changing practices.
What you disclose.
What you deliver.
BUSINESS-SPECIFIC PRIVACY COUNSEL
A policy grounded in
the way you do business.
A privacy policy is a public-facing explanation of your personal information practices. Its requirements depend on the information involved, your activities, and the laws that apply. Drafting starts with understanding those facts.
Build an accurate policy.
We assess your website or app, business model, users, vendors, and data flows to prepare appropriate disclosures. The goal is language that fits your practices and addresses relevant legal requirements.
Find gaps and mismatches.
We review existing policies, including template-based and AI-generated drafts, for omissions, outdated language, unsupported promises, and inconsistencies with the tools and services you use.
Connect notice with action.
We advise on related terms, cookie disclosures, consent and opt-out tools, rights-request procedures, vendor agreements, and policy updates. The engagement scope determines the implementation support included.
We can assess whether it still reflects your operations and the legal requirements relevant to your business.
Ask about a review ↗THE LEGAL LANDSCAPE
Different laws.
A coherent approach.
A useful assessment distinguishes the laws that apply to your business from provisions copied into a policy merely because they appear elsewhere.
U.S. state privacy requirements
Comprehensive state privacy laws, including California’s CCPA as amended by the CPRA, have differing coverage rules and obligations. Other notice, consumer protection, and data-specific laws may matter even when comprehensive-law thresholds are not met.
Explore our state privacy law tracker ↗EU, UK & international practices
Where applicable, GDPR and UK requirements call for assessment of transparency, lawful bases, individual rights, and cross-border transfers. The locations of your users and activities matter alongside where your company is based.
Explore GDPR counsel ↗Children & teenagers
COPPA focuses on children under 13, while other laws may address teenagers and use different age ranges. Audience, age knowledge, collection methods, and parental or school involvement require a fact-specific assessment.
Explore children’s privacy counsel ↗Health & sensitive information
Health, financial, biometric, and other sensitive information may raise additional requirements. A health-related app or website needs an assessment of the relevant laws rather than an assumption that HIPAA is the only consideration.
Explore health privacy counsel ↗REAL-WORLD CONSEQUENCES
When privacy promises
and practices diverge.
Privacy policy issues can lead to regulatory scrutiny, private claims, and loss of trust. These examples show why accurate language and operational follow-through need to work together.
Match Group & OkCupid
The FTC’s March 2026 case concerned allegations that OkCupid shared photos and location information with an unrelated third party contrary to its privacy promises.
Verify that data transfers, including AI-related uses, match your disclosures and commitments.
TikTok
The UK ICO imposed a £12.7 million fine in 2023 for data protection failures, including unlawful use of children’s information. In September 2026, the ICO announced that TikTok had withdrawn its appeal against the fine.
Children’s privacy requires an assessment of your audience, age controls, lawful processing, and appropriate consent where required.
Healthline
California’s July 2025 settlement addressed allegations involving tracking, advertising disclosures, opt-outs, and inadequate contractual protections. Article titles could reveal sensitive information about readers.
Review the information trackers transmit, the way opt-outs function, and what downstream contracts require.
Tractor Supply
California’s September 2025 order addressed multiple alleged CCPA failures, including a privacy policy that went years without an update. Policy maintenance formed part of a broader compliance assessment.
Review both legal requirements and actual practices. Changing a “last updated” date alone does not correct inaccurate or incomplete disclosures.
Sonos
Reporting on Sonos’s 2024 privacy policy changes illustrates how changes to public-facing data commitments can attract scrutiny even when a company offers assurances about its practices.
Consider how users will understand a policy change. Clear explanations and consistent practices are part of preserving trust.
Adobe
In June 2024, Adobe announced clarifications to its terms following concerns about content rights and AI. The company said it had not trained generative AI on customer content and would explain its commitments more clearly.
Coordinate AI disclosures, content licenses, privacy statements, and the actual uses of information.
PRIVATE CLAIMS MATTER, TOO
Policy wording is only part of tracking risk.
Claims involving the California Invasion of Privacy Act (CIPA), the Electronic Communications Privacy Act (ECPA), and the Video Privacy Protection Act (VPPA) can raise issues beyond comprehensive privacy law thresholds. Analytics, pixels, session replay, and embedded video tools deserve review alongside notice, consent, and actual data flows.
Automated scans can help identify trackers and potential inconsistencies with public disclosures. A scan is a starting point for review, rather than a substitute for legal analysis.
A privacy policy does not automatically authorize every tracking activity or eliminate litigation risk. Public-facing disclosures should be assessed together with the technology and user interface.
WHAT YOUR POLICY MAY NEED TO COVER
The disclosures behind
the document.
Your industry, business size, users, jurisdictions, and processing activities shape the required content. These are common areas of assessment, rather than a universal checklist.
Information collected
Names, contact details, IP addresses, device and browsing data, transactions, and sensitive categories such as health or financial information.
Sources & collection methods
Forms, accounts, cookies, pixels, integrations, vendors, and other third-party sources. What is collected directly and what arrives from elsewhere?
Purposes & lawful bases
Service delivery, payments, personalization, analytics, marketing, and other uses. Identify relevant lawful bases where the applicable framework requires them.
Recipients, sales & sharing
Service providers, advertisers, analytics vendors, and other recipients. Distinguish ordinary disclosures from regulated “sale” or “sharing,” where applicable.
Rights & request methods
Applicable access, correction, deletion, portability, objection, appeal, and opt-out rights. Explain usable request methods and relevant preference signals.
Retention
How long information is kept, or the criteria used to determine retention, consistent with the business’s actual processes and applicable requirements.
Security
Appropriate descriptions of safeguards without unsupported guarantees or unnecessary exposure of security-sensitive details.
Children & teenagers
Audience, age ranges, collection practices, and any required parental notices or consent. A statement that a service is “not for children” may not settle the analysis.
International transfers
Cross-border transfers and applicable safeguards. Where relevant, assess mechanisms such as standard contractual clauses or eligible Data Privacy Framework participation.
Updates & contact details
How users can contact the business and how material changes will be communicated. Review whether additional notice or consent is required for a particular change.
AI & model training
Whether personal information is used, disclosed, or made available for AI or large language model training. Assess specific state disclosure rules and their effective dates alongside the underlying processing requirements.
A policy should include what your business needs and avoid language that describes practices you do not follow.
FROM NOTICE TO OPERATIONS
The policy, the tools,
and the experience must align.
Publishing a document is one part of privacy compliance. A policy review can also reveal decisions needed about the tools, interfaces, and internal processes behind your disclosures.
Cookies & consent
Cookie notices and controls should reflect the actual technologies deployed. Assess whether consent or opt-out is required, when tools fire, and whether user choices are honored in practice.
Cookie compliance & consent counsel ↗Terms & related agreements
Coordinate contractual commitments, data-use provisions, and acceptance flows. A privacy policy is generally a notice; agreeing to website terms does not automatically provide every privacy or marketing consent required by law.
Terms & conditions counsel ↗Rights requests & vendors
Explain rights users can actually exercise and assess the processes behind them. Vendor contracts should support appropriate handling, restrictions, and cooperation with requests.
Privacy rights & DSAR counsel ↗Platforms & ongoing review
Consent-management and privacy tools need appropriate selection and configuration. Review the policy when practices change, and track any periodic update obligations that apply.
Explore privacy & consent platforms ↗THE VALUE OF LEGAL JUDGMENT
Accuracy over boilerplate.
A longer policy is not necessarily a better policy. The useful question is whether it accurately addresses your practices and the requirements relevant to your business.
TAILORED LEGAL COUNSEL
A policy informed by your operations.
- Business-specific assessment of data practices and applicable laws.
- Clear disclosures and review of unsupported or unnecessary promises.
- Advice on cookies, consent, terms, and related implementation issues.
- Consultation to explain relevant obligations and practical next steps.
- Ongoing advice as your products, tools, and legal requirements evolve.
GENERIC OR COPIED POLICIES
Assumptions that need review.
- Language that may describe another business’s practices.
- Missing disclosures or promises your business cannot meet.
- Limited analysis of jurisdictional and industry-specific requirements.
- No assurance that the policy matches your tracking technologies.
- No built-in process for keeping disclosures and operations aligned.

A RICHT OFFERING
Explore PrivacyExpress™.
Learn more about RICHT’s privacy policy offering.
Explore PrivacyExpress ↗SCOPE & FEES
A clear scope.
A practical starting point.
Fees depend on the complexity of your data practices, the users and jurisdictions involved, and whether you need drafting, a targeted review, or broader privacy support.
We offer flat fees for agreed scopes. Existing policies can be reviewed and updated, with related terms, cookie compliance, and implementation advice included where agreed.
Discuss scope and fees ↗COMMON QUESTIONS
Privacy policies,
explained.
What is the history of privacy policies?
Public-facing privacy notices developed as businesses increasingly collected personal information online. The core transparency question remains the same: what information is collected and what happens to it? Modern laws add more detailed requirements concerning rights, uses, recipients, and accountability.
What should a privacy policy include?
The answer depends on the business and applicable law. Common subjects include information collected, sources, purposes, recipients, rights, retention, contact details, and relevant international transfers. Children’s information, sensitive data, advertising, and AI-related uses may require additional treatment.
What are the dangers of copying or generating a generic policy?
The policy may omit important disclosures, describe practices you do not follow, or create unsupported commitments. Inaccuracies can contribute to regulatory or private claims, depending on the facts and applicable law. Copying another company’s text can also raise intellectual property concerns.
Is a lawyer legally required to draft a privacy policy?
A lawyer is generally not legally required. Whether a generated policy is suitable depends on your processing activities, obligations, and risk profile. Counsel can help assess those issues and coordinate the policy with your tools, contracts, and procedures.
How should a business communicate material policy changes?
Review applicable law, existing commitments, and the nature of the change. A revised date or posted document may not be sufficient. Some changes require prominent notice, additional consent, or a separate assessment of whether a new use of previously collected information is permitted.
Does a privacy policy replace a cookie banner or consent process?
No. Disclosures, consent, and opt-out mechanisms serve related but different functions. Whether a banner or another interface is required depends on the technologies, processing activities, users, and applicable law. Controls should function consistently with the policy.
How often should a privacy policy be reviewed?
Review it when material practices change and on a schedule suited to applicable legal obligations. New vendors, tracking tools, AI features, audiences, or markets can all require reassessment. A review should verify the substance, not simply update the publication date.
Can RICHT review an existing website or app privacy policy?
Yes. We can assess your existing policy against the practices and legal requirements relevant to your business, identify issues, and agree an appropriate scope for revisions or related advice.
START A CONVERSATION
Bring your business.
We’ll help clarify the privacy obligations.
Tell us about your website or app, users, data practices, and whether you need a new policy or an existing-policy review.
Explore our privacy compliance risk evaluation tool.
Use the assessment ↗PRIVACY POLICY RESOURCE HUB
Explore the issues
behind the disclosures.
WATCH / RICHT EXPLAINS
Privacy Policy Compliance Explained and a Lawyer’s Role
WATCH / FEATURED VIDEO
A closer look at privacy law.
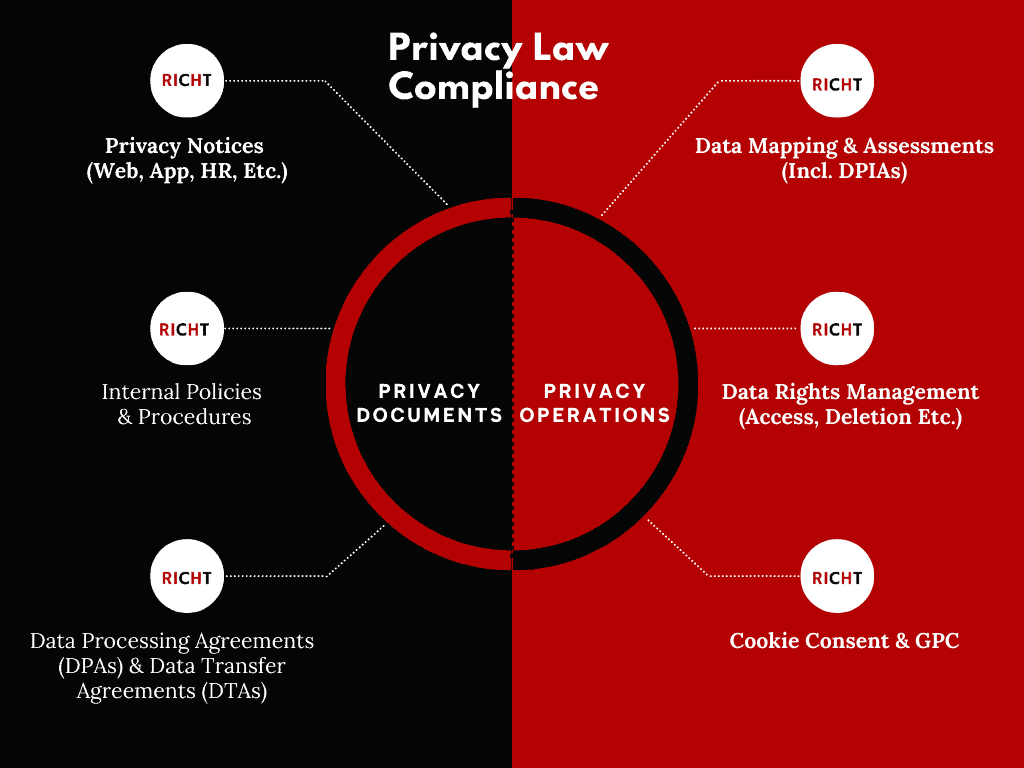 Click to enlarge ↗
Latest Insights
Privacy policy insights.
Recent analysis of privacy notices, enforcement actions, and the practices behind the disclosures.

AI’s Next Data Source Is Your Business: The Privacy Questions Behind the Training Data Market
An advertisement makes the proposition unusually clear: “You’ve got 3 years of emails, invoices, and business records doing nothing. We’ll pay you six figures for them.” For a…
Read insight
Webull’s China Scrutiny: Why U.S. Data Storage Is Only Part of the Compliance Picture
Congressional scrutiny of Webull brings renewed attention to the relationship between data residency, foreign access, corporate…

FTC Takes Action Against OkCupid and Match Group for Sharing User Photos with a Facial Recognition AI Company
On March 30, 2026, the Federal Trade Commission filed a complaint in the U.S. District Court…
Selected news & resources
Resources retained from this practice page. Each reflects its original publication context.
PRIVACY NOTICES
Business website privacy notices
A practical resource on when a business needs a public-facing notice and how a data inventory supports accurate disclosures.
Start with the actual data practices. A policy can only be as accurate as the information used to prepare it.
TRACKING LITIGATION
Privacy notices and statute-of-limitations defenses
Commentary on how discoverable privacy disclosures may affect timeliness arguments in website wiretapping litigation.
Preserve prior notices and publication records. Their role in a limitations defense differs from contractual acceptance or valid privacy consent.
FEDERAL PRIVACY CLAIMS
ECPA claims and policy inaccuracies
A discussion of theories invoking ECPA’s crime-or-tort exception in disputes over data collection and privacy representations.
Review written disclosures against tracking behavior. Litigation theories and available defenses depend on the facts and jurisdiction.
FTC ENFORCEMENT
Match Group & OkCupid privacy promises
The FTC proceeding concerns allegations of data disclosures inconsistent with public privacy commitments.
Assess the permitted uses and recipients of information before sharing it, including for AI-related purposes.
CALIFORNIA REQUEST RIGHTS
California’s “Shine the Light” trap
Commentary on litigation risks and request-handling requirements associated with California’s direct-marketing disclosure law.
Assess whether this distinct law applies and ensure relevant disclosures and request procedures work in practice.
AUSTRALIAN PRIVACY
Privacy policies under the spotlight
The OAIC’s announced compliance sweep highlights privacy notices in businesses that collect information in person.
A privacy policy assessment should account for offline collection as well as website and app activity.
CALL RECORDING
Neon and call-recording privacy concerns
Reporting on privacy concerns involving a call-recording app and the handling of conversations and associated information.
Recording features deserve assessment of consent, access, retention, security, and downstream uses.
DIRECT MARKETING
A wave of “Shine the Light” requests
A further resource on California request rights and the processes businesses use to address them.
Train relevant teams to recognize different request types and apply the correct procedures and timing.
POLICY MAINTENANCE
CCPA annual-update requirements
A reminder to assess the periodic disclosure-update requirements applicable to covered businesses.
Keep an accountable review process that checks both the policy and the practices it describes.
MOBILE APPLICATIONS
CNIL’s mobile-app recommendations
French regulatory guidance addressing privacy considerations in the design and operation of mobile applications.
Review app permissions, SDKs, data flows, and notices together. Website-focused disclosures may not describe app behavior adequately.
UK ICO Releases Privacy Notice Generator For SMEs
To ease compliance and notification burdens for U.K.-based small- and medium-sized enterprises, the Information Commissioner’s Office officially launched its Privacy Notice Generator. The tool offers SMEs an easy step-by-step process that will create tailored privacy notices that are geared toward the business’s specific role in the U.K. economy.
How to Quickly Get to the Important Truth Inside Any Privacy Policy
Privacy policies can be long, impenetrable, and full of legalese that amounts to a take it or leave it offer. But the privacy policy is one of the only places where you can find the truth about what personal data is being collecting or otherwise processed.
Don’t Date Robots — Their Privacy Policies Are Terrible
Research from Mozilla found many AI companion apps fail privacy checkups and often don’t stand by what their chatbots ask of users.
Five Big Questions For The U.S. State Privacy Law Landscape in 2024
Exploring five big questions about the state privacy landscape that will shape how 2024 legislative developments will impact the protection of personal information in the United States.
How Threads’ Privacy Policy Compares to Twitter’s (and Its Rivals’)
Here’s what personal data is collected by Meta’s Threads, as well as by Twitter, Bluesky, Mastodon, Spill, and Hive Social.
TikTok Fined £12.7m For Illegally Processing Children’s Data
TikTok has been fined £12.7m for illegally processing the data of 1.4 million children under 13 who were using its platform without parental consent, Britain’s data watchdog said.
Here’s What You’re Actually Agreeing To When You Accept a Privacy Policy
Almost every new app or product that is connected to the internet forces you to accept a long, indecipherable privacy policy in order to use it. These documents outline the company’s data-collection practices. But what exactly are you agreeing to when you accept?
White House OSTP publishes report on privacy-preserving data sharing, analytics strategy
The U.S. White House Office of Science and Technology Policy released a report on a “National Strategy to Advance Privacy-Preserving Data Sharing and Analytics.”
Facebook’s WhatsApp Fined For Breaking The E.U.’s Data Privacy Law
Regulators in Ireland, where many tech giants have their European headquarters, have been criticized for not enforcing Europe’s data-protection law, once heralded as a global standard.
The State of Consumer Data Privacy Laws in the US (And Why It Matters)
The United States doesn’t have a singular law that covers the privacy of all types of data. Instead, it has a mix of laws that go by acronyms like HIPAA, FCRA, FERPA, GLBA, ECPA, COPPA, and VPPA.